eSignature for IT: What Your Procurement Team Is Not Asking
Victor Grund, VP Solutions Engineering, Vasion
September 9, 2026
7 mins
An eSignature decision rarely starts with IT. It surfaces in a business unit, gets framed around pricing metrics and brand recognition, and reaches IT only at the security and integration review, after the shortlist is set. By then the comparison has been shaped by what the vendors compete on, and they compete hard: signing experience, templates, routing, dashboards, AI. All of it is real, all of it demos well, and almost none of it is where the friction and the risk sit.
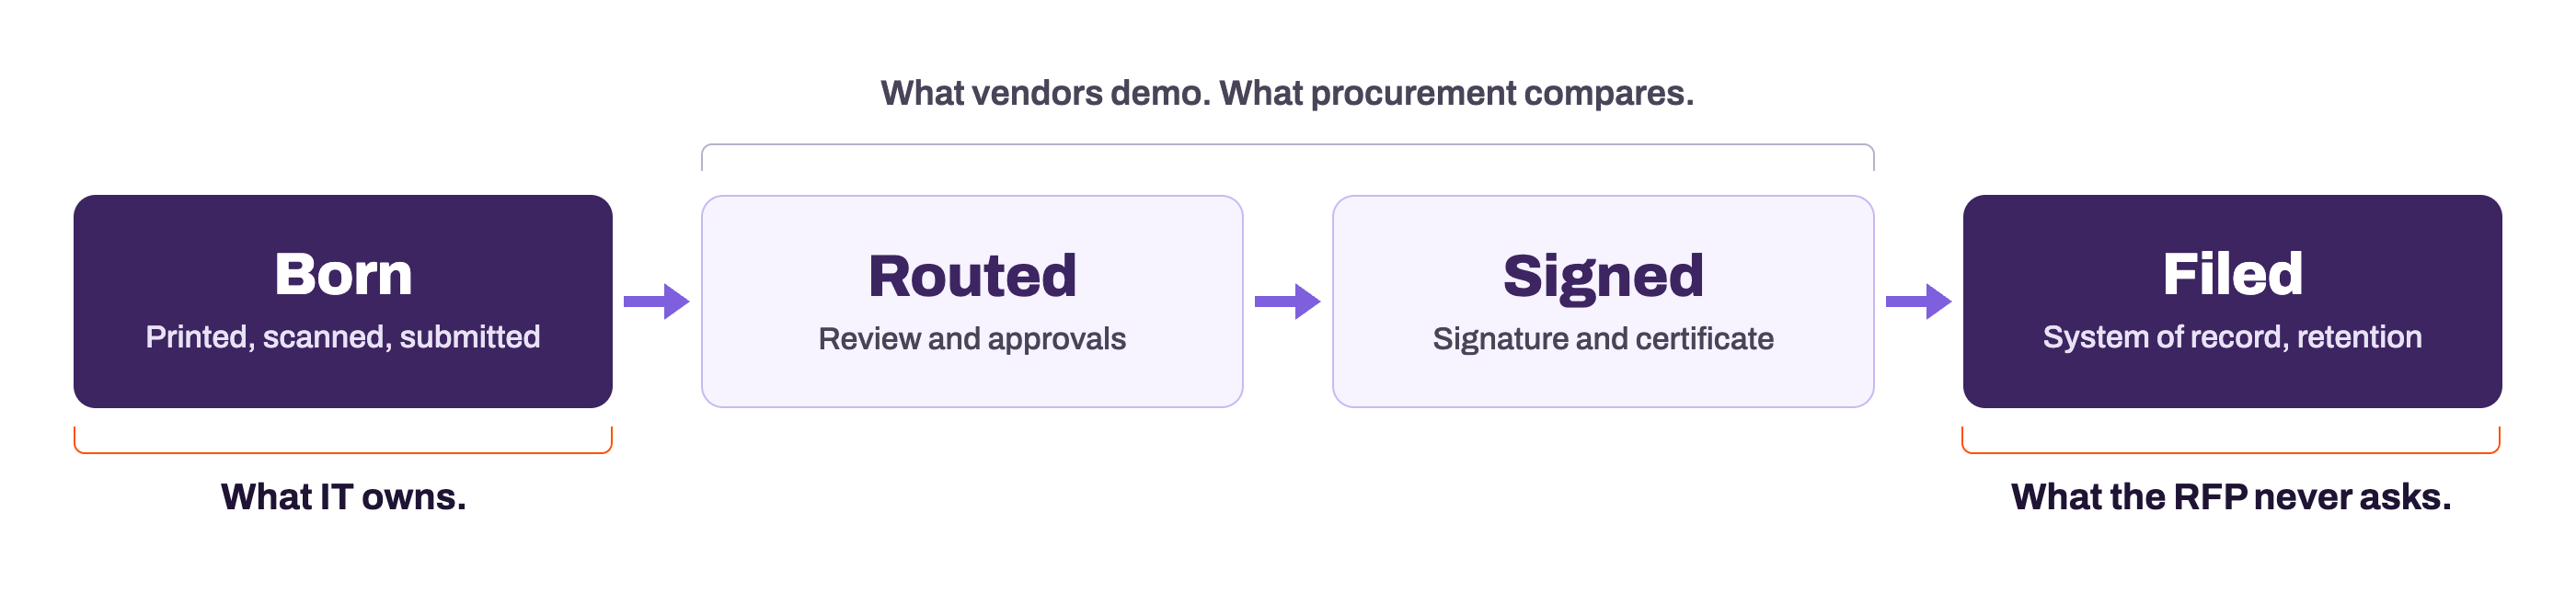
A signature is one step in a longer process. A document is created or captured, routed for review, signed, and filed. The question that predicts success is not which signing tool is cheapest per seat. It is where signing fits in the processes you already run, and whether one platform can own the steps around it. These are the questions IT should add before an eSignature contract is signed.
The Middle Is Well Served. The Edges Are Not.
Look at that sequence again: created or captured, routed, signed, filed. Every serious signing platform is excellent in the middle. Whether the vendor leads with signing, with document generation, or with workflow around the signature, the middle of the document's life is a competitive, mature, well-demoed market. Procurement can compare the middle on its own, because the middle is what the pricing page describes.
The differences that decide whether the system works best in production sit at the two edges: where the document is born, and where it must end. No signing vendor owns the edges. IT does. That is why the edge questions never appear in the RFP, and why they surface later as integration projects, manual workarounds, and a second system nobody budgeted.
 The Entry Edge: Where Documents Are Born
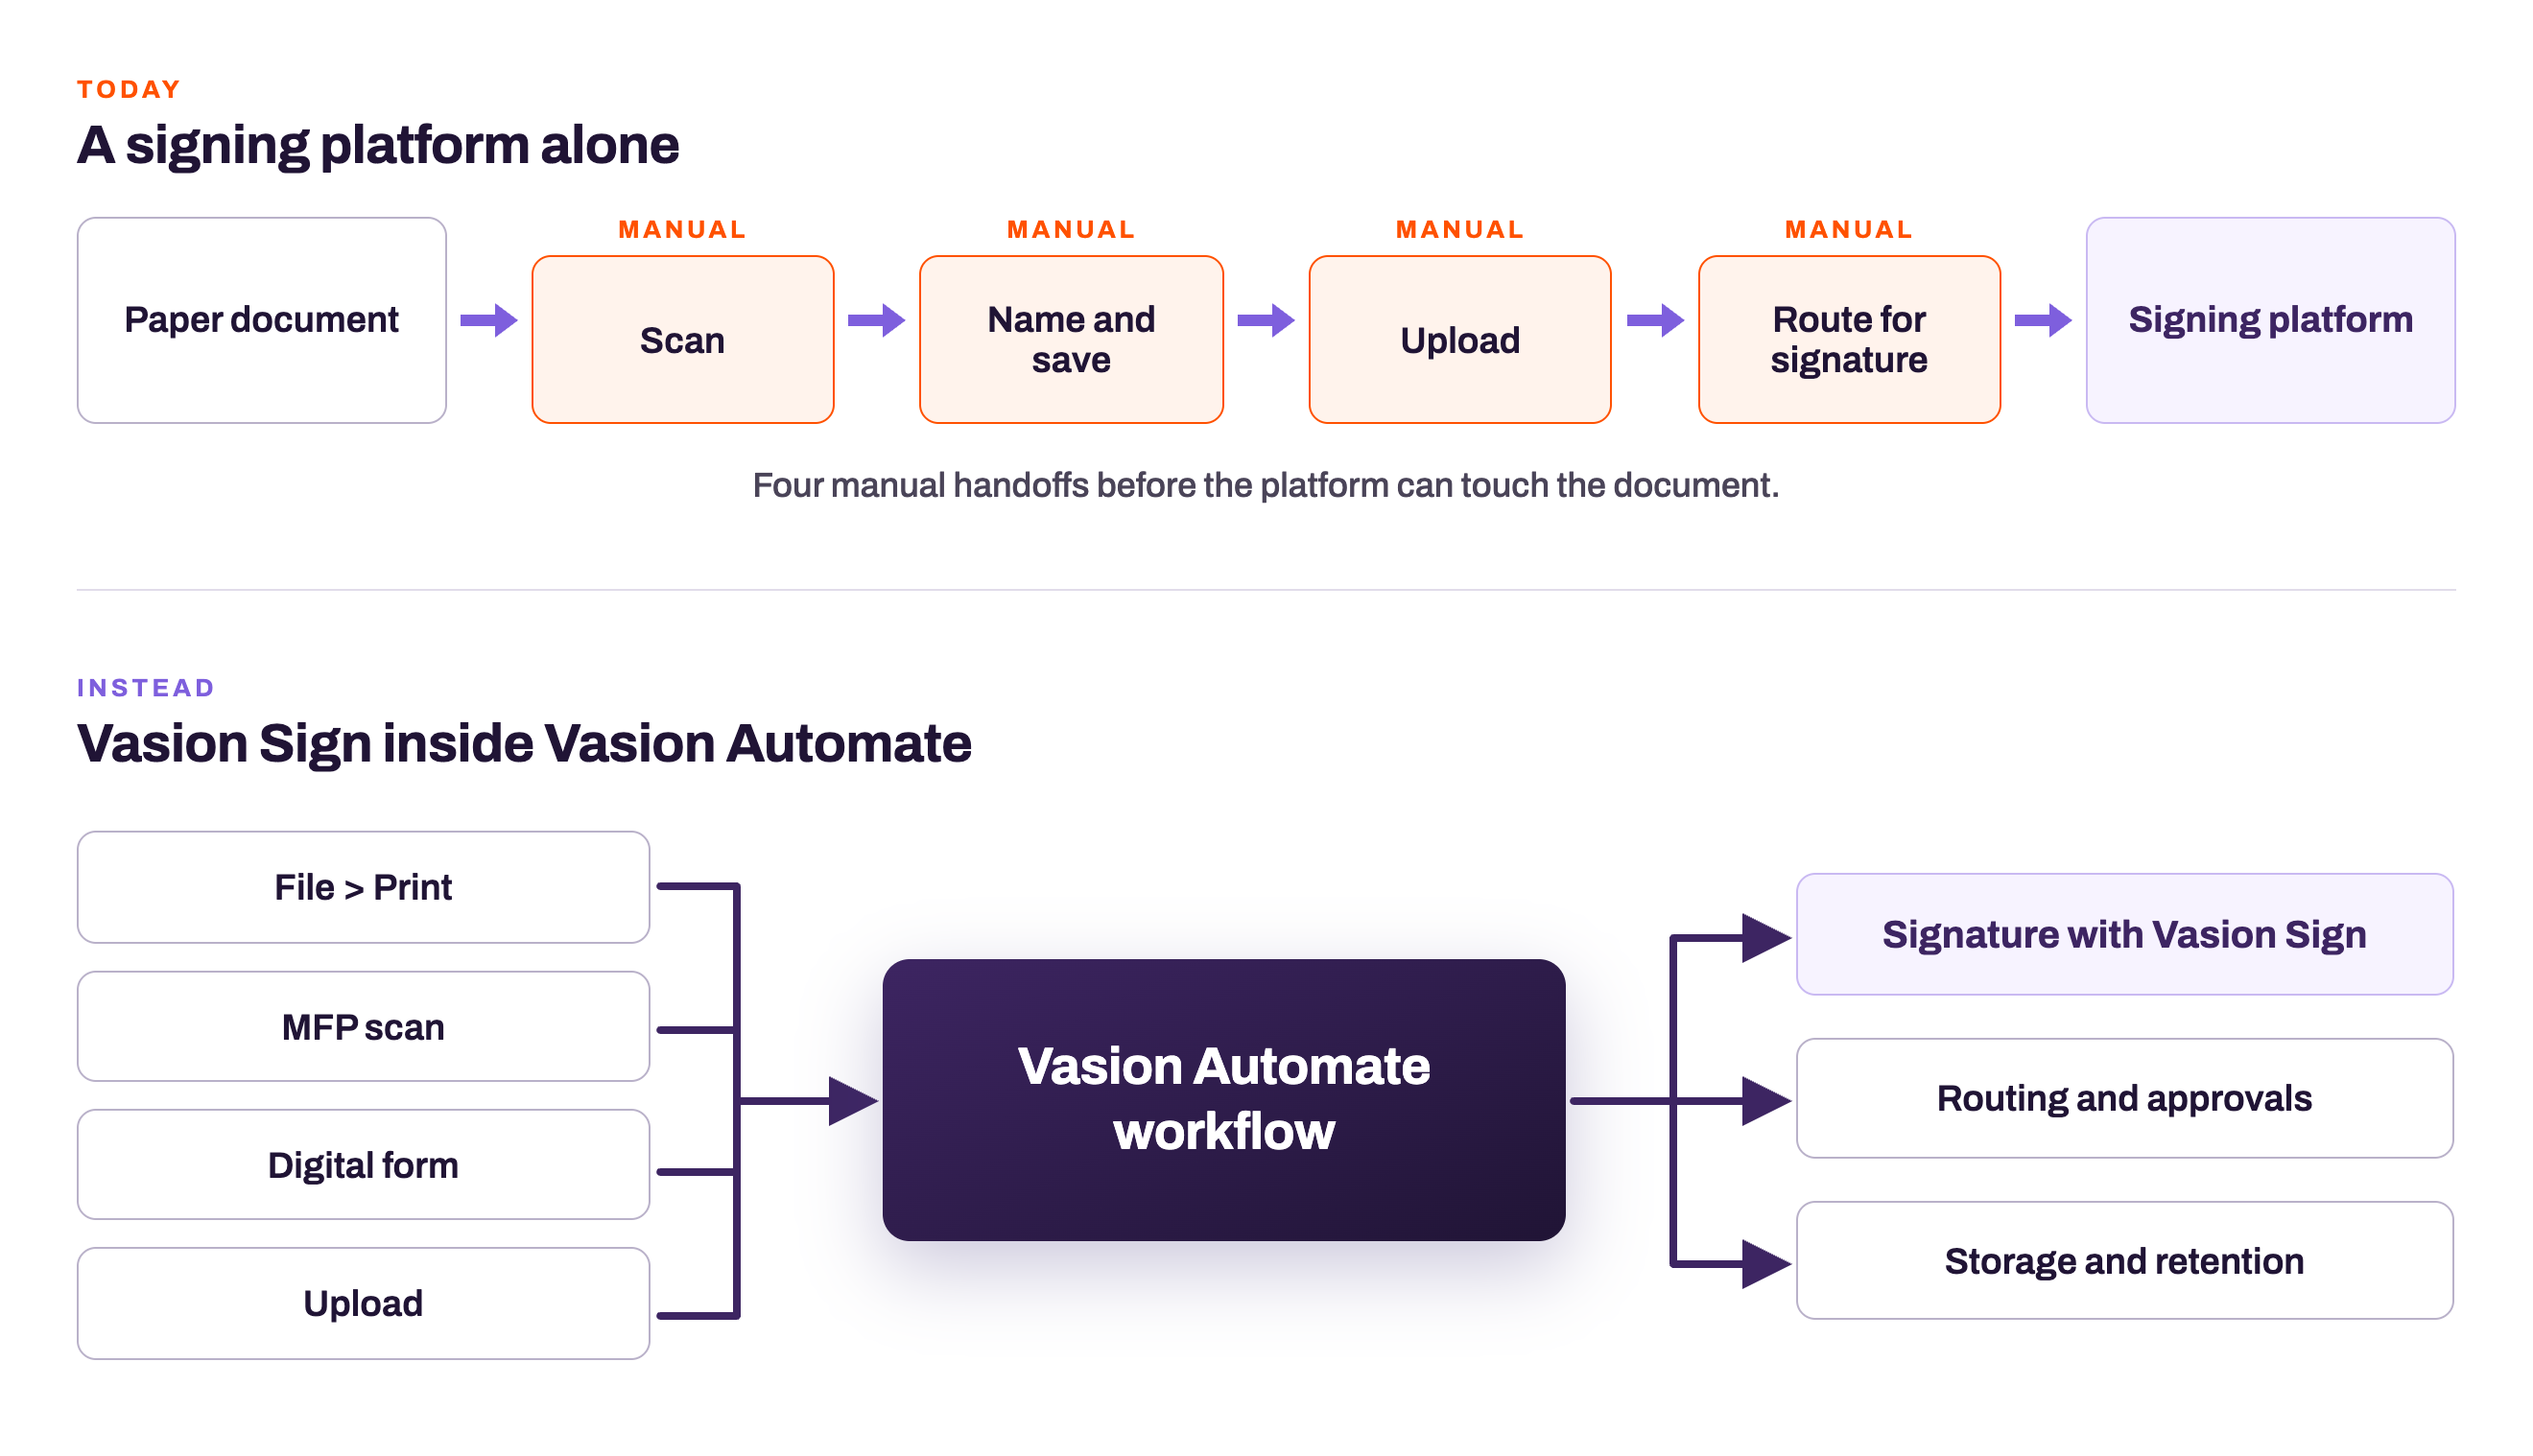
Every signing platform assumes the document starts digital. Either someone uploads a finished file, or the platform generates one from a template and data. For a sales quote or a standard contract, that assumption holds. For much of what an organization signs, it does not. Consent forms, field authorizations, HR packets, and intake paperwork are often born on paper or at a device: printed, handed over, scanned. Before any signing platform can touch that document, someone must digitize it, name it, upload it, and route it. That manual gap is invisible in a per-seat quote and very visible in daily operations.
Ask two questions at this edge. First, what share of the documents that need signatures today begin as something printed or scanned? Second, what is the native path from the print dialog or the MFP into a signing request, and is that path built in or bolted on through middleware that IT then owns?
Vasion Sign is built at this edge. Because it lives inside Vasion Automate, a document can enter from the File > Print dialog, from an MFP scan, from a digital form, or from an upload, and route directly to signature as one branch of a defined workflow. Print to Sign turns the everyday print action into the signing trigger, with no separate upload step and no change to how people already work.
The pattern is established in healthcare, where patient intake and consent forms route from the same File > Print action clinicians already use into workflows, signature, and secure archival, with no change to the clinical routine. The gains are measurable: Caregiver, a Vasion customer, went from a form approval process that could take a minimum of one week to a couple of hours after digitizing it.
 The Exit Edge: Where the Process Finishes
Most signing platforms end at a signed file and a certificate, stored in the vendor's repository. The process ends later. The signed document must reach the system of record, retention must be applied, and the data inside it often must reach downstream systems. Ask who moves the document there, how many systems touch it between signature and final storage, and whether a completed document can trigger the next step or waits for a person to notice it.
The exit edge also includes the documents that never need a signature. Invoices, intake forms, permits, and records must be captured, routed, and filed with the same discipline as anything signed, and a platform organized around signing leaves those to a second system. If signing is the only document process the platform runs, you have automated one workflow and left the rest where they were.
In Vasion Automate, signature is one branch of a general document process, not the end of it. Conditional routing, parallel approvals with configurable merge behavior, an approval send-back that returns a form to the submitter without restarting the workflow, and automatic filing into storage with configurable retention are part of the same platform. Intelligent Document Processing (IDP) can extract structured field data from a document, and route low-confidence extractions to human review, whether or not that document ever reaches a signature step.
Cost Accrues at the Edges
The middle is priced transparently: a seat price, a plan tier, a usage allowance. Edge costs are quieter. Capabilities beyond core signing, such as digital forms, identity verification, SMS and bulk sending, and API access, are frequently priced as add-ons beyond the seat, whether the plan caps documents or advertises them as unlimited. Ask how usage is counted, whether it is capped, and which of the capabilities you need are priced separately.
Then count the costs no quote shows. The labor of digitizing and routing born-paper documents by hand. The middleware and integration work to bridge the entry and exit edges. A second system for the documents that never get signed. And the standalone contract itself: one more vendor, one more integration, one more license to manage. A quote that looks competitive for one department can look very different once signing spreads to HR, operations, and the field, and once the edge costs arrive.
When signing is a capability of a platform you already run, most of those line items shrink or disappear. Vasion Sign folds into the Vasion Automate platform, so consolidation removes a signing vendor instead of adding one.
The Connection to What IT Already Runs
Two infrastructure questions round out the evaluation. The first is identity. Separate authentication, which proves the signer controls an account or an inbox, from identity verification, which proves the signer is a specific real person. For internal and transactional signing, the priority is binding the signature to your identity provider through single sign-on, so signers authenticate against the directory that already governs your environment rather than a standalone user list. Ask for SAML 2.0 or OIDC support with provisioning through your identity provider, and weight high-assurance verification only for the documents that need it, with its per-use cost on the table. Vasion Sign integrates through SAML 2.0 and OIDC with just-in-time provisioning.
The second is the audit record. Treat it as a floor to verify, not a differentiator to chase. Confirm what is captured per event: signer, action, timestamp, and originating IP at minimum, with a certificate of completion that is generated automatically and is tamper-evident. Then confirm control: who sets retention, whether an administrator can alter or delete a completed record without a log entry, and whether documents are encrypted at rest and in transit to a recognized standard such as FIPS 140-2. Vasion Sign records person, action, timestamp, and IP for every event and generates the certificate automatically, and Vasion Automate holds SOC 2 Type 2 and ISO 27001:2022, and supports HIPAA compliance requirements.
The Question Underneath All of Them
Few organizations should buy a platform only to get eSignature, and that is the point. Evaluated on the middle, every credible vendor looks strong, because the middle is where they all live. Evaluated edge to edge, from the moment a document is born to the moment it is filed, the field narrows fast, and the question changes. It stops being which signing tool wins the demo and becomes which platform can own print, capture, forms, workflow, storage, and signature together, under one administration and one security model.
The questions below are ready to drop into your next RFP. To see the entry edge working, walk through the interactive Vasion Sign demo, and confirm the certifications and identity-verification options that apply to your deployment with the Vasion team.
Questions to Add to Your Evaluation
- Entry: What share of documents needing signatures begin as something printed or scanned, and what is the native path from print dialog or MFP into a signing request?
- Entry: Is that path built in, or middleware that IT then owns?
- Exit: After signing, who moves the document to the system of record, and can completion trigger the next step automatically?
- Exit: How does the platform handle documents that never need a signature: invoices, intake forms, permits, records?
- Cost: How is usage counted, is it capped, and which capabilities are priced as add-ons beyond the seat?
- Cost: What do the edges cost: manual digitization labor, middleware, and a second system for unsigned documents?
- Identity: Does authentication bind to our identity provider through SAML 2.0 or OIDC, and what does high-assurance verification cost per use where required?
- Audit: What is captured per event, is the certificate automatic and tamper-evident, and who controls retention?
- Compliance: Does the signing capability itself carry SOC 2 Type 2 and ISO 27001, will the vendor sign a Business Associate Agreement where PHI is involved, and are documents encrypted at rest and in transit to a stated standard?
- Platform: Can one platform own print, capture, forms, workflow, storage, and signature under one administration and security model?