For print environments, segmentation is crucial in preventing compromised devices from accessing other systems or sensitive data across your network. By breaking your infrastructure into isolated zones, you can limit exposure and reduce the impact of any potential breach.
What It Means
Segmentation means creating strategic boundaries that make it much harder for attackers to move freely or access sensitive data. There are two main ways to do this:
Network Segmentation (Microsegmentation): Divides your network into small, isolated zones. In print environments, this means isolating printers on dedicated network segments with controlled access points, so a compromised device can’t easily reach other resources.
Architectural Segmentation (Serverless Printing): Eliminates centralized print servers, allowing direct device-to-printer connections. While related to microsegmentation, it’s an architectural choice that reduces centralized points of failure.
Note: It’s not all or nothing. You can implement network segmentation even with print servers in place, and you can also adopt serverless printing without full network segmentation. Both approaches enhance security—but combining them gives you the strongest protection.
Why It Matters
Segmentation is vital for keeping breaches from getting out of control. Most organizations (about 96%) use some form of network segmentation, but very few (around 2%) have thoroughly segmented all their mission-critical areas, including printers.
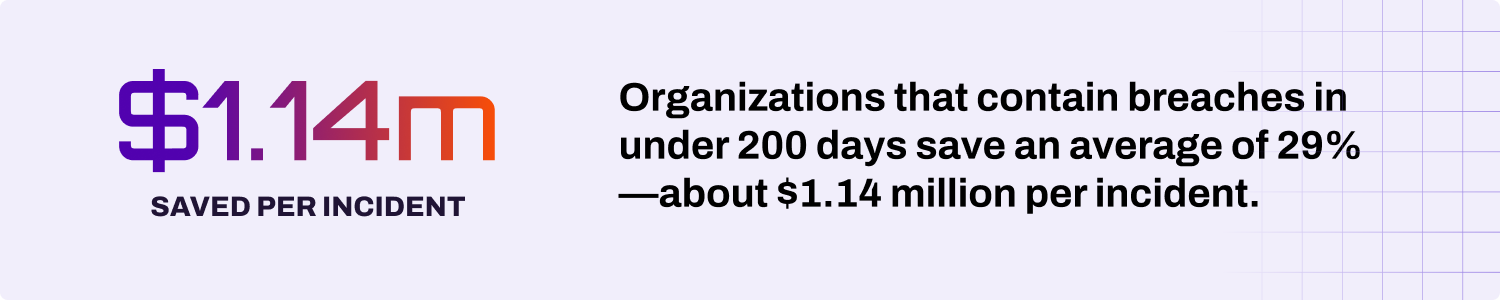
That means printers are often among the least protected systems, leaving them vulnerable to potential attacks. Proper segmentation helps close that gap, making it easier to contain breaches when they do occur. In fact, IBM research found that organizations that contain breaches in under 200 days save an average of 29%, translating to about $1.14 million per incident.
 Implementation Best Practices
Implementing segmentation is where Zero Trust really starts to pay off. Here are the concrete steps you need to protect your printers and reduce risk:
Network-Level Segmentation:
Place printers on isolated network segments or VLANs
Separate print traffic from general network traffic
Implement access control lists (ACLs) at network boundaries
Restrict unnecessary printer-to-printer communication
Apply Zero Trust network access (ZTNA) principles to print traffic
Architectural Approaches:
Eliminate or reduce dependence on centralized print servers where feasible
Use direct device-to-printer connections
Implement secure cloud-based print management where appropriate
(Even if your organization still needs print servers for certain legacy applications or workflows, you can still apply Zero Trust principles using other security controls.)
Data Protection Strategies:
Encrypt print jobs in transit and at rest
Implement automatic data deletion policies after job completion
Use secure release printing to prevent sensitive documents from sitting in output trays
Ensure printer hard drives are encrypted or regularly wiped
User-Level Access Controls:
Implement role-based printer access
Separate guest printing from employee printing
Create department-specific print queues with appropriate access controls
Limit access to high-security printers (check printing, confidential documents)
Real-World Application
If a device gets compromised, proper segmentation keeps the problem from spreading. Attackers can’t use your print system to reach other users’ data or move throughout the network. Instead, the breach stays contained to that single endpoint, keeping both your printers and the rest of your network safe.