Problem #1: Operators can't install the printer they need
On a plant floor, those who need to print don’t always have admin rights. Since Microsoft's August 10, 2021 updates, Windows requires administrator privilege by default to install printer drivers, a change made to address CVE-2021-34481. That default is correct for security. It also sends every new printer, replaced label printer, and shift-change workstation to the helpdesk.
The tempting workaround is worse. Microsoft cautions that setting the RestrictDriverInstallationToAdministrators registry value to zero "makes devices vulnerable," and says no combination of other mitigations is equivalent to leaving it enabled. Plants with shared PCs, contractors, and multiple shifts end up choosing between delayed printing and weaker security.
Problem #2: Jobs go to the wrong printer, or nowhere
Shared kiosks, roaming supervisors, and multi-building sites mean the default printer might be the wrong one. Queues are typically mapped by group policy to a print server, and those mappings drift. A printer is replaced, a server is retired, a team changes buildings, and the old queue stays on the workstation. The operator prints, nothing comes out, and they print again to a different queue.
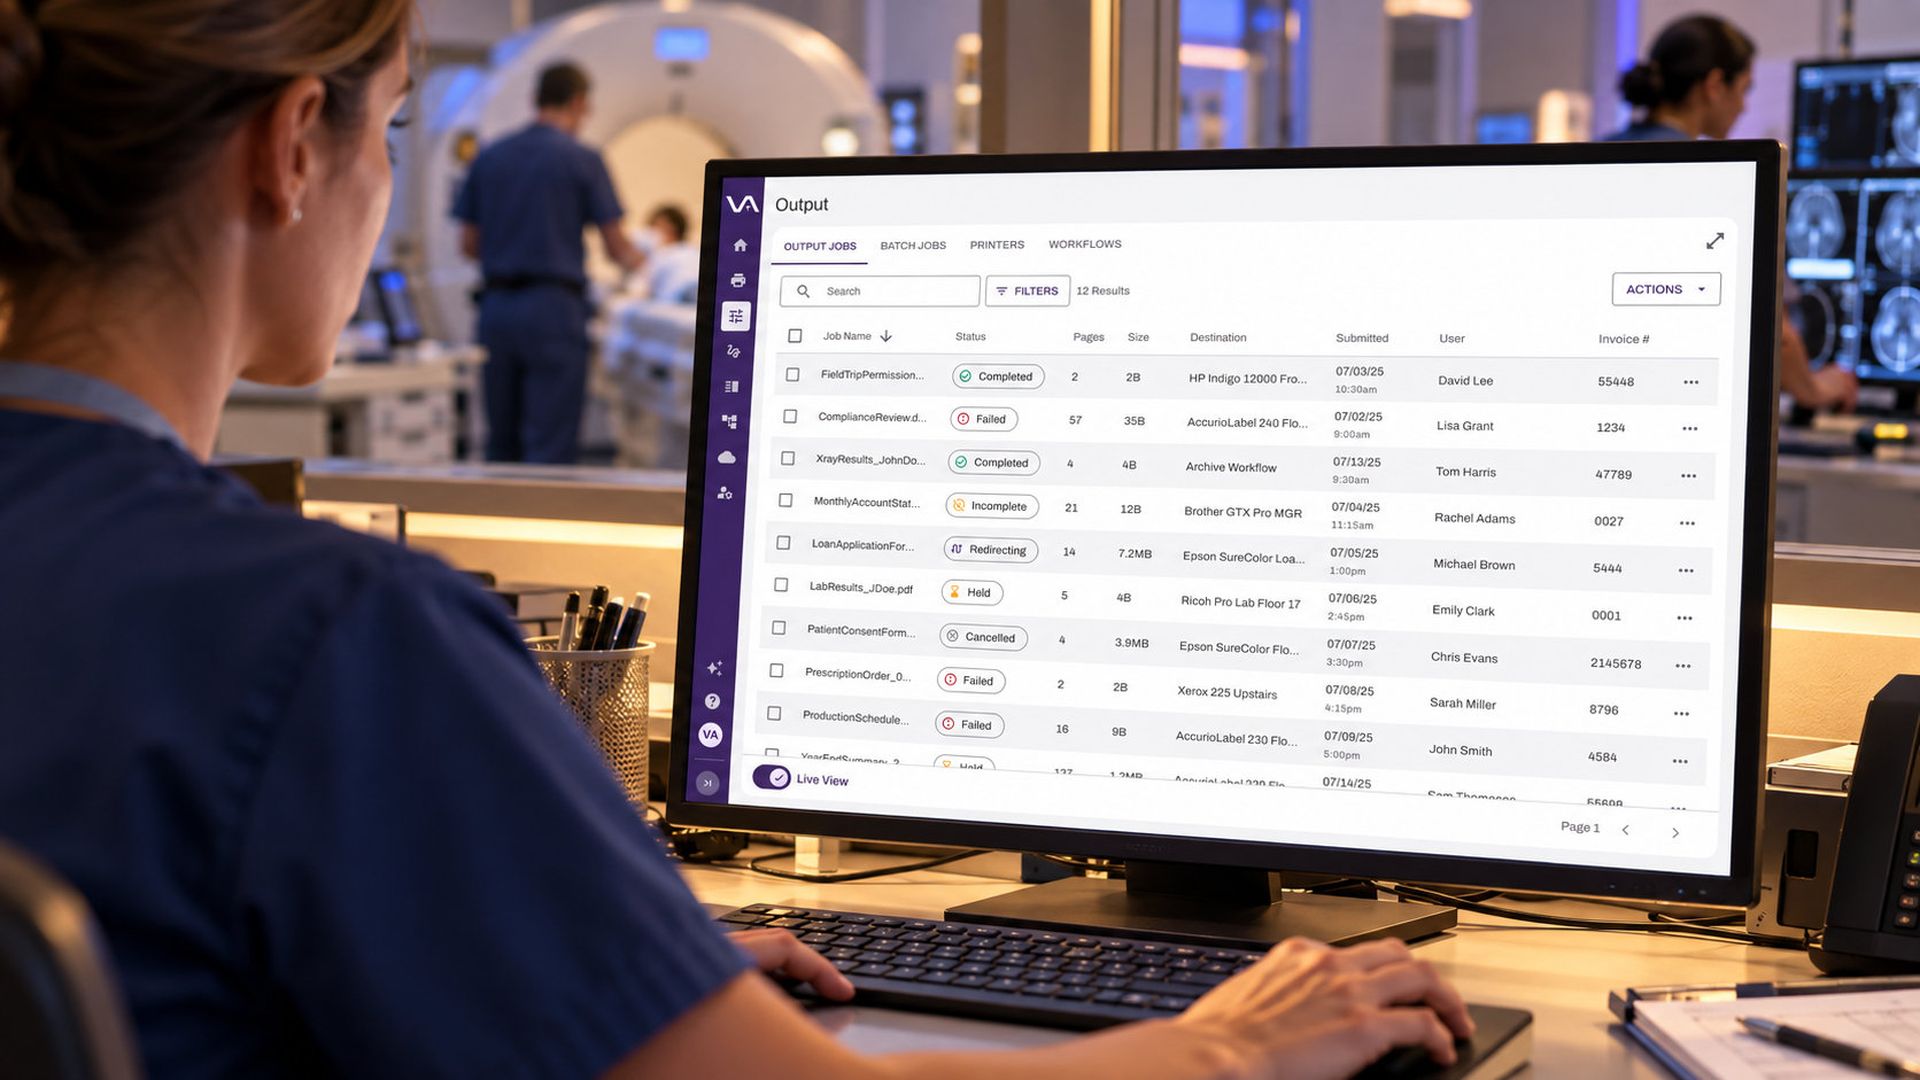
The result is duplicate jobs, missing paperwork at the station, and a ticket that starts with "which printer did you send it to?" On a three-shift line, a stale mapping can sit unnoticed until the one person who prints a lot traveler or quality checklist comes on shift. The underlying issue is visibility: a user at a workstation has no easy way to tell whether a job is queued, stuck, or headed for a device that was unplugged last quarter.
Problem #3: Sensitive documents sit in the output tray
Plants print documents that should not sit in an open tray: engineering drawings, supplier pricing, batch records, HR paperwork, and controlled technical data. A shared printer in a corridor or on the shop floor turns each of those jobs into an unsupervised handoff, and anyone walking past can pick it up.
Secure release, where a job waits until its owner authenticates at the device, is the standard answer. It works best when it is part of how printers are deployed and managed, not a separate project layered over a print server estate that was never designed for it. Without it, uncollected jobs also pile up as wasted paper and toner.